A sovereign platform for your agents. Securely run by RAW Labs.
We set up Enterprise OpenClaw, OpenClaw and OpenClaw Enterprise as one supported platform, where you need it. Then we keep it secure and up to date: vetted skills, tested updates, monitoring.
We design it around your data.
Before anything is installed, we decide with your security team where the platform runs, how people sign in, and which model may see which data.
- Your cloud, on premises or ours
- The sign‑in you already use
- Data only to the models you allow
We deploy it closed by default.
Each team’s agents run in a space of their own that refuses any traffic a rule doesn’t allow, and each agent can do only what you approved.
- The fewest rights possible
- Only the software we tested
- Secrets never in settings or logs
We vet every skill before it gets in.
Skills are add-ons that let agents do new things, and anyone can publish one. A safe one can turn harmful in its next version. So we check each skill before your agents may use it, give it only the access it needs, and pin the version you approved.
-
Malicious skills
Anyone can publish one, and some send data out.
-
Poisoned updates
Safe today, harmful in tomorrow’s version.
-
Hidden instructions
Prompt injection that code scanners miss.
-
Too much access
Broad permissions widen the damage.
We run it for you.
Once it is live, we keep it running for you, on the terms we agree.
- Watched, incidents handled
- Backed up, restored when needed
- Model spending within your limits
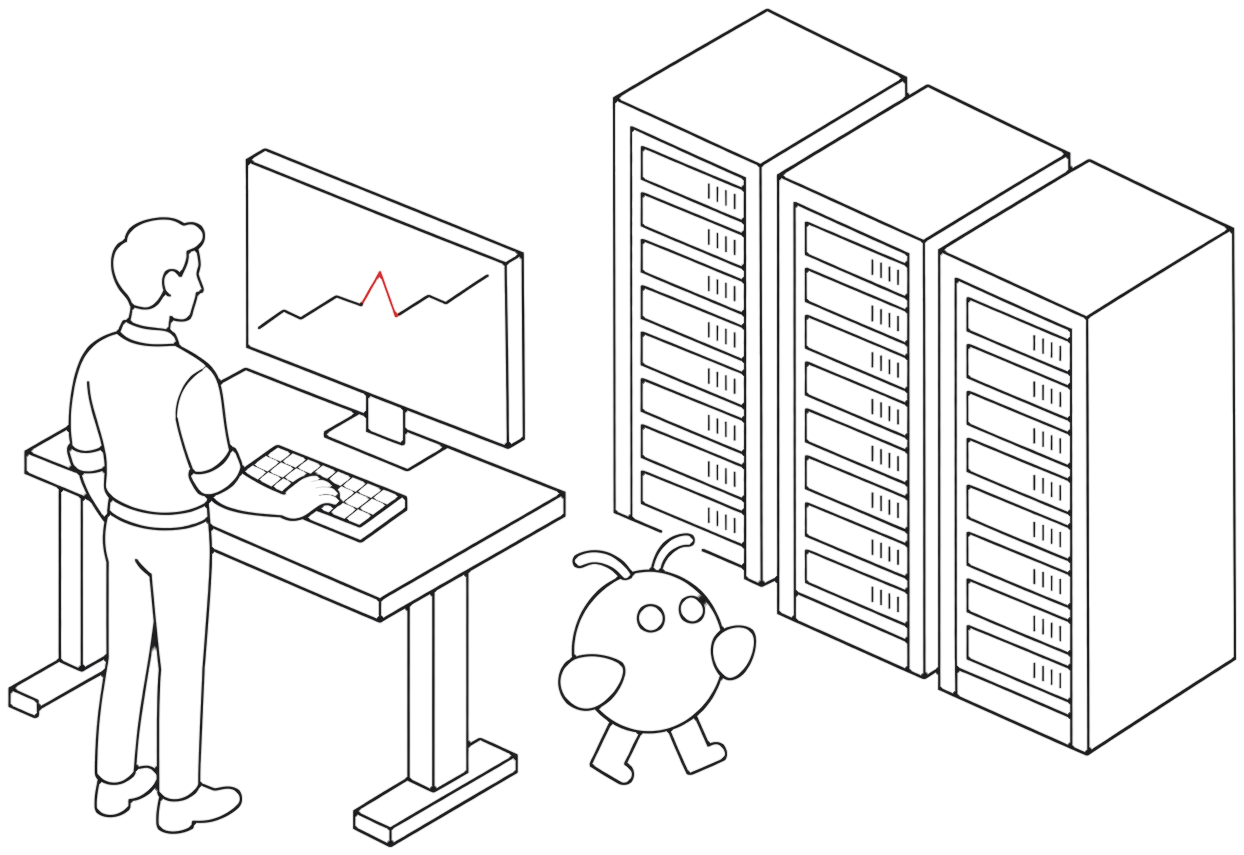
We test every update on your work first.
We watch for vulnerabilities, run your own skills and workflows against each new release, and roll it out in stages.
Every release lists exactly which versions of OpenClaw Enterprise and OpenClaw it contains. All releases
We keep the evidence your auditors ask for.
We map the platform’s controls to the frameworks you report against and document them from its own record of who changed what.
- Controls mapped to your frameworks
- Documented from its own record
- Tested from outside every year
Three layers. One team.
We start with the work, set up your teams’ workspaces, then deploy the platform it all runs on.
-
Agentic operating model
For the business.
-
Agentic workspaces
For your teams.
-
Sovereign & secure platform
You are here
-
OpenClaw Enterprise
Open source, with no lock-in.